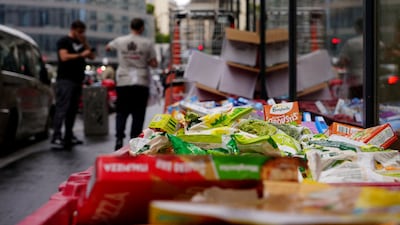

The Iranian hackers accused of attacking supermarket refrigerators in Europe exploited flaws in similar equipment used in the US and the UK.
The French authorities launched an investigation on Monday into Shahid Kaveh, which is part of the cyber and electronic command of Iran’s Islamic Revolutionary Guard Corps and is under sanctions from the US.
Hamid Lashgarian, its chief, was placed under sanctions in 2024 by the US. Washington has offered a $10 million reward for information about his activities.
Prosecutors in Paris say the hackers went after the supermarket refrigeration controllers made by Danfoss and Dixell, affecting about 700 mass retail sites in France.
The activities of Shahid Kaveh in hacking the type of technology used in the supermarket fridges was first highlighted in late 2023.
A joint warning was issued by the Cybersecurity and Infrastructure Security Agency, the FBI, the UK’s National Crime Agency, the Environmental Protection Agency, the Israel National Cyber Directorate and the Canadian Centre for Cyber Security.
It said Shahid Kaveh had compromised programmable logic controllers made by Israel-based Unitronics.
The PLCs are industrial-grade computers designed to automate machinery, manufacturing lines and critical infrastructure.

They are used in water and wastewater, energy, food and drink, manufacturing, health care and other industries, including refrigeration.
This year, the CISA, FBI and other US federal agencies said more PLCs had been compromised in an attack that had similarities to the one carried out by Shahid Kavah.
It was aimed at industrial control devices used in critical infrastructure targets including the energy sector, water and wastewater utilities, and unspecified “government facilities".
If unaddressed, the hacks could affect the water, wastewater treatment and energy sectors.
The UK’s National Cyber Security Centre, which is a branch of the signals intelligence agency GCHQ, sent out an alert to energy companies after Shahid Kaveh shut down an energy site in July.
The Department for Energy Security and Net Zero has insisted the attack was on a small plant that did not pose a risk to the wider energy system.
“In response to this specific incident, the NCSC and Department for Energy Security and Net Zero briefed energy CEOs and directly wrote to companies with advice, direction and next steps,” said a representative.
“The UK has a highly resilient energy system. We work closely with the energy sector to protect infrastructure and ensure the highest security standards."
A recent report by cybersecurity company Tenable found that CyberAv3ngers has “repeatedly compromised small water utilities, municipal facilities, and rural energy operators, and the reason is structural, not coincidental”.
Tenable said many of these organisations using remote access tools that expose their PLCs “directly to the public internet,” making them vulnerable to attack.