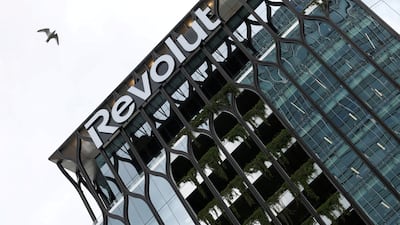

Cybersecurity experts say lessons must be learnt from an incident in which digital banking platform Revolut was deceived into turning over private customer data to hackers.
The UK-based financial technology firm, with more than 80 million customers, confirmed someone posing as an Italian government regulator by email succeeded in procuring identification card information, photos, account statements, transaction histories and other items of data from the company.
Some reports suggest the hackers are already leaking that information and demanding Revolut pay a ransom to prevent more of the data being revealed.
In a statement provided to The National, a spokesperson for the company said that Revolut contacted the individuals impacted to inform them of the situation and provide the needed support.
"Revolut recently identified a sophisticated external impersonation scam where an unauthorised third party utilised a legitimate government agency domain email to submit fraudulent requests for information," the statement read in part.
"Upon detection, we immediately blocked the address and alerted the relevant government agency as well as enforcement agencies, data protection, and financial regulators," the company explained, adding that Revolut's systems and customer funds have not been impacted.
Technology experts and cybersecurity analysts say the type of attack could become more popular among criminal groups.

“Nobody broke into Revolut's systems, the attackers asked for the data and the bank sent it,” said Ivan Milenkovic, vice president for cyber risk technology at IT security firm Qualys.
Though the criminals hacked an Italian government's email system to pose as law enforcement, they also took advantage of human nature, Mr Milenkovic said.
“The weak point was the [Revolut] desk that answers police requests and how much it trusts a government domain,” he said. The list of information stolen, which reportedly includes passports, driving licences and verification selfies, was particularly worrisome, he added. “You can reset a password in a minute but you can't reset your face.”
Santiago, a threat-intelligence research lead at Acronis, reflected on how what initially seemed to be merely a data breach turned into extortion, with the hacker believed to have asked for about $3 million in a blockchain-based cryptocurrency.
Although Revolut said it had received no “direct demand”, Mr Pontiroli said “the public countdown increased the pressure on the bank and affected customers”.
For too long, this type of phishing has been viewed as something older and less technically minded people fall for, he added.
“Evidence demonstrates this stereotype is outdated and anyone can be deceived when an approach fits the context and arrives through a channel they already trust,” Mr Pontiroli said.
In the Revolut case, he said “the apparent targets of the deception were employees responsible for handling official information requests, not elderly or inexperienced consumers”.
Art Gilliland, chief executive of Delinea, which specialises in digital data and identity security, said it was counterproductive to reduce such attacks to a question of technical literacy.
“The request … carried strong signals of legitimacy and authority that many experienced professionals could reasonably find convincing,” he said.
Mr Gilliland said because reports indicate about 650 Revolut customers were affected, the attack was probably “not to collect as much data as possible, but to identify individuals whose information could provide the greatest leverage”.
He said lessons can be learnt from the incident by even the most seasoned cybersecurity experts, companies and organisations.
“Organisations cannot make employees, no matter how tech savvy they may be, the final line of defence,” he said. “A legitimate email domain should never be sufficient proof on its own and sensitive requests need independent verification, appropriate approval and controls that restrict both, who can access the information, and how much can be released.”
Similar incidents on smaller scale
Revolut is not alone in being targeted like this.
Technology, culture and philosophy expert Joan Westenberg recently detailed what she described as a social engineering attempt disguised as a podcast that expressed interest in booking her as a guest.

“Their prep was impeccable with better interview questions than most journalists,” she posted on social media platform Threads. The individuals provided a link that asked her “to run a terminal command to install their webinar tool”, causing her to spot the hacking attempt and stop communicating.
Ms Westernberg said the cyber criminals continued to pressure her to participate in the process and later harassed her when she stopped responding. “Never, ever install custom software for a meeting or podcast,” she wrote.
Mr Pontiroli said this is an example of what cybersecurity experts describe as “ClickFix-style social engineering”, which is becoming an increasingly a popular choice among state-sponsored hackers in North Korea.
“The victim is persuaded to execute malware under the pretext of installing software or fixing a technical problem,” he said. “The screenshots and subsequent harassment also appear designed to pressure the target into ignoring their doubts.”
He added that although the tactic is not new, the proliferation of artificial intelligence has made it much easier to execute.
“While there’s no indication that AI was used in this particular case, it’s making similar attacks cheaper, faster and easier to scale,” he said.